Certificate Lifecycle Management: Swiss Post Cybersecurity Brings Order to the Certificate Jungle
Swiss Post Cybersecurity uses Certificate Lifecycle Management (CLM) to automate the management of digital certificates throughout their entire lifecycle. Hosted in Switzerland, the solution provides IT teams with a centralized overview of certificates, responsibilities, and expiration dates, thereby reducing security risks posed by expired or non-compliant certificates.


Digital certificates are the invisible foundation of modern IT infrastructures. They enable encrypted communication, authenticate systems, and build trust between applications, devices, and services. At the same time, managing them is becoming increasingly complex: The number of certificates is rising sharply, and in some companies, the number of machine identities is already 60 times higher than that of human identities.
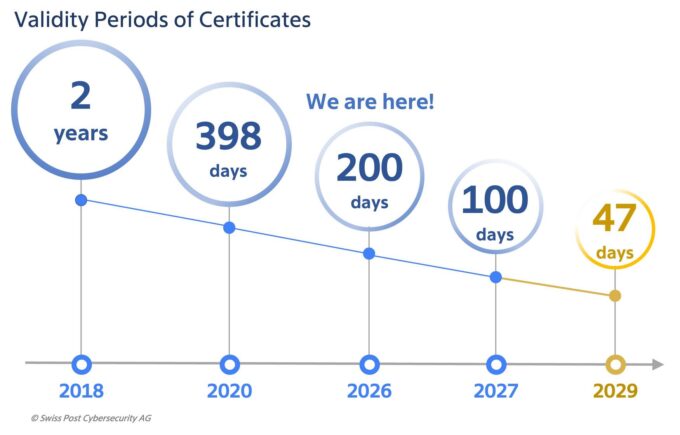
The validity period of certificates is also decreasing significantly. In 2018, it was still two years; today, it is 200 days, and by 2029, it will be only 47 days. At the same time, regulatory requirements for monitoring and traceability are increasing. Furthermore, the transition to post-quantum cryptography will require the replacement of thousands of certificates.
For IT departments, this means more work and a growing risk of security vulnerabilities. An expired certificate can block access, cripple applications, disrupt business processes, and, in the worst-case scenario, increase a company’s attack surface.
Swiss Post Cybersecurity addresses these challenges with its automated Certificate Lifecycle Management (CLM). The solution provides transparency into all certificates and automates recurring processes. «Certificates are among the things in IT that should function as invisibly as possible. If a team has to regularly check whether a certificate is about to expire somewhere, that’s a sign that too much is being done manually,» says Paul Such, CEO of Swiss Post Cybersecurity. «With Certificate Lifecycle Management, companies regain control over their certificate landscape—before expired, misconfigured, or non-compliant certificates jeopardize operations.»
A Centralized Overview Instead of Certificate Chaos
Swiss Post Cybersecurity’s CLM solution tracks certificates across different architectures, consolidates them into a central inventory, and can leverage existing PKIs. This provides IT teams with an overview of which certificates are available and where they are used, who owns them and who is responsible for renewal, when they expire, and where action is needed—for example, regarding compliance issues or weak algorithms. Risks such as unauthorized certificate authorities or violations of defined policies can be identified early on.
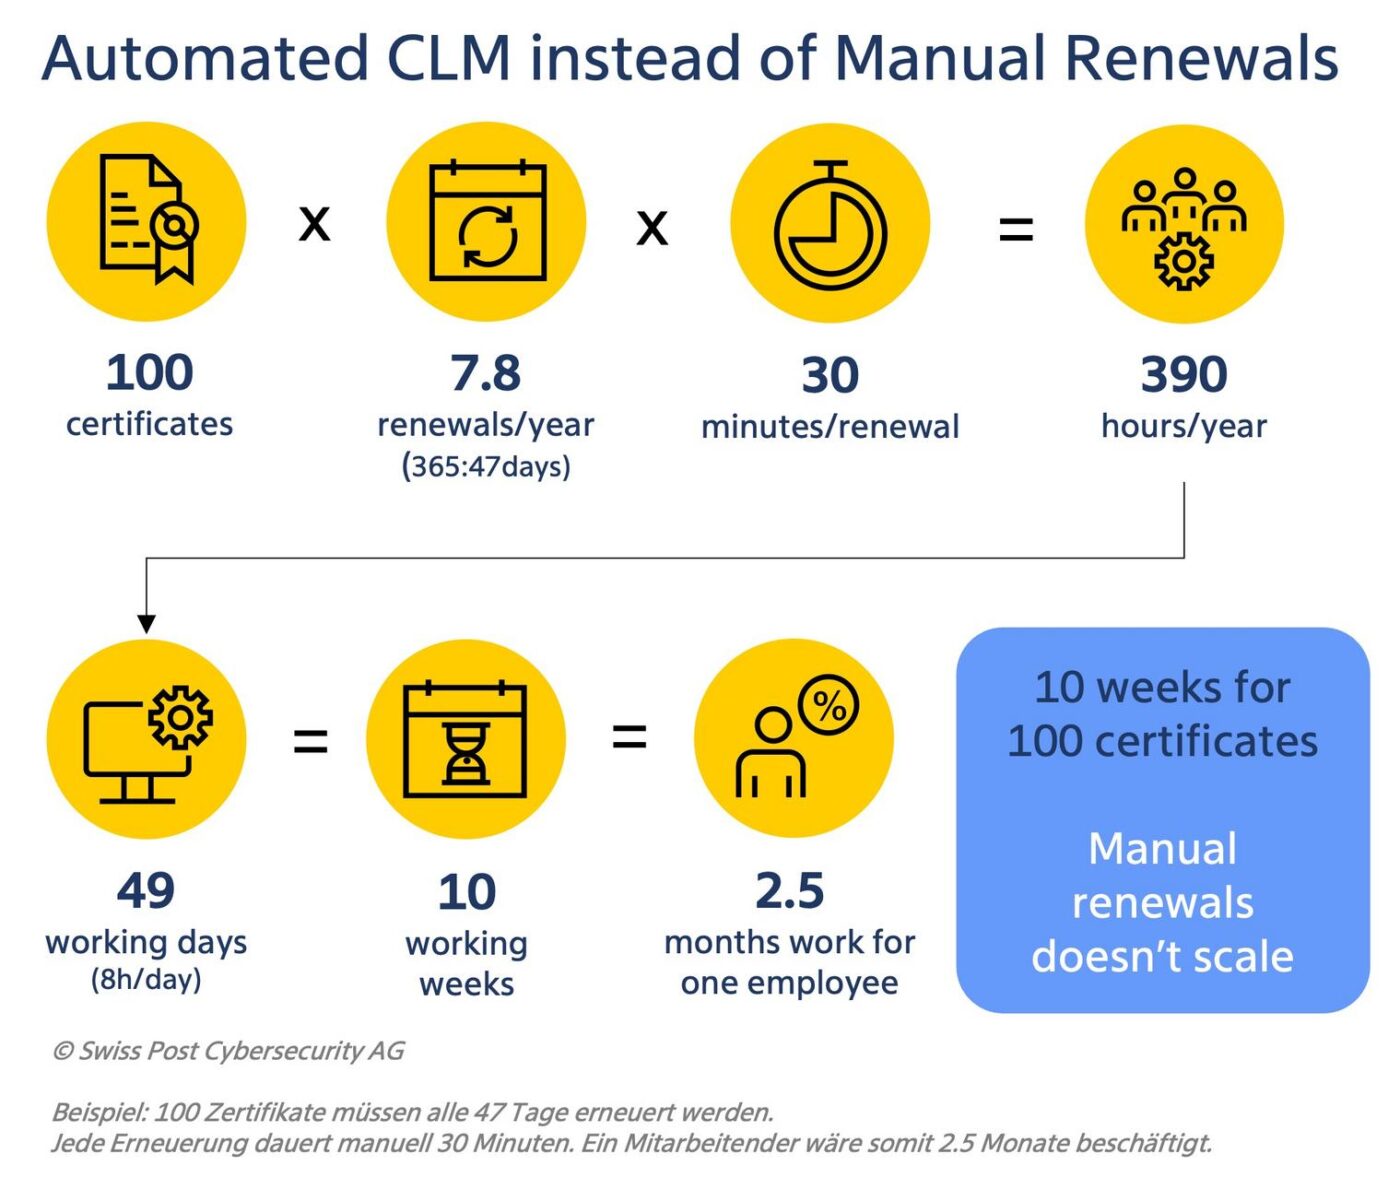
CLM automates the entire lifecycle—from issuance to renewal to revocation. This reduces repetitive tasks and eliminates sources of error. Notifications, defined policies, and automated workflows ensure that certificates are not an issue only after a system outage has already occurred.
Thorough Preparation for Audits and Compliance Reviews
Certificates are an integral part of the security architecture and, as such, are increasingly becoming a governance and compliance issue. Centralized inventory tracking and transparent management help companies monitor their assets and better meet audit requirements.
The Swiss Post Cybersecurity solution offers features in the areas of auditing, governance, and automation to support this. This enables organizations to define responsibilities and permissions, map approval processes, and enforce policies. For companies subject to regulatory requirements such as NIS2 or DORA, structured certificate management thus becomes a key component of their security organization.
European technology, Swiss operations
Swiss Post Cybersecurity’s CLM solution is based on the platform from Evertrust, a French provider of cybersecurity solutions that SwissSign also relies on. Swiss Post Cybersecurity has been an authorized implementation and hosting partner since May 2026. The CLM instances are hosted on Swiss Post Cybersecurity’s private infrastructure in Switzerland.
Certificate Lifecycle Management refers to the centralized management of digital certificates, from issuance through monitoring and renewal to expiration or revocation. The goal of CLM is to eliminate the need for manual certificate management and instead manage certificates centrally, according to defined rules, and automatically throughout their entire lifecycle.
Swiss Post Cybersecurity AG offers security solutions to protect companies’ digital information and confidential data and helps them meet increasing security requirements. In particular, the Cyber Defense Center’s SOC services are developed and provided in Switzerland. Expertise in governance, offensive security, integration, and risk & compliance rounds out the offering. With approximately 150 employees, the company serves over 350 organizations in Europe. Its headquarters are located in Aarau, with additional offices in Morges and Luxembourg. Swiss Post Cybersecurity AG is an independent, market-oriented subsidiary of Swiss Post and was formed in 2024 through the merger of the two market leaders, terreActive and Hacknowledge.
https://www.swisspost-cybersecurity.ch/de/