Swiss Cyber Storm 2026: Former U.S. Lieutenant General Karen Gibson Opens Conference on Shadow IT
Swiss Cyber Storm 2026 will take place on October 20 at the Kursaal in Bern and will focus on the theme of «Shadow IT.» The opening keynote will be delivered by former U.S. Lieutenant General Karen H. Gibson, who previously served as the U.S. Senate’s Chief of Security. The full conference program, covering topics ranging from artificial intelligence to quantum computing, is now available online.


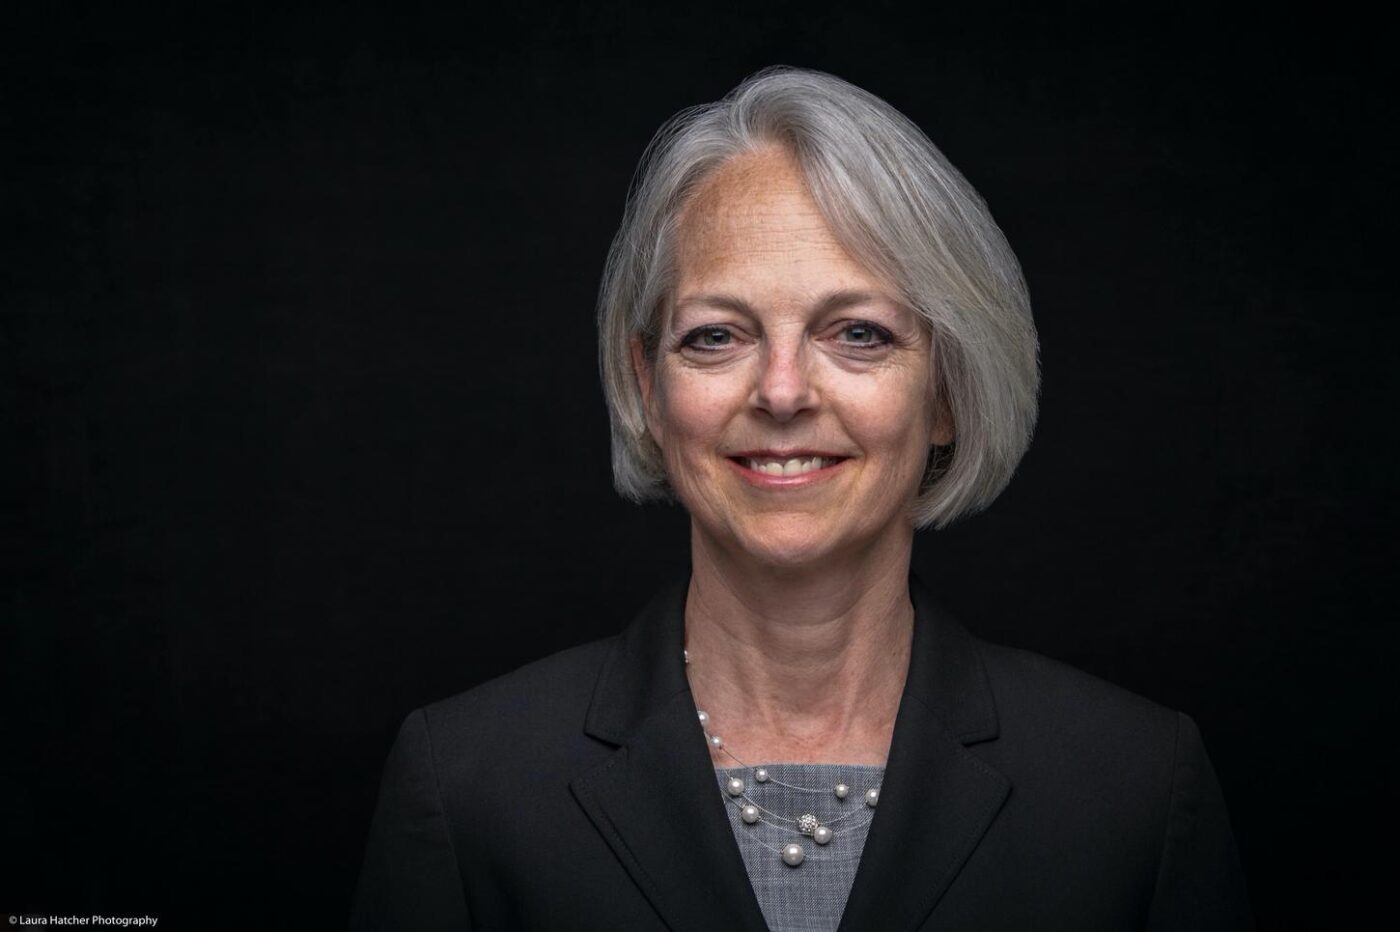
Retired U.S. Lieutenant General Karen H. Gibson will deliver the opening keynote address at Swiss Cyber Storm 2026. The IT security conference will take place on October 20 at the Kursaal in Bern, and this year’s focus will be on «Shadow IT.» The full conference program is now complete and available at https://www.swisscyberstorm.com/schedule/.
Experience from the U.S. Senate
Karen Gibson served as the 42nd Chief of Police of the U.S. Senate from 2021 to 2025. She was appointed following the January 6 attack on the Capitol and served as the Senate’s top official responsible for law enforcement, protocol, and security. Under her leadership, the physical security, government continuity, and cybersecurity programs underwent a fundamental overhaul, including the protection of 450 Senate offices throughout the United States.
Gibson’s keynote address is titled «Seeing the Shadows: Securing What You Don’t Control.» Drawing on her experience securing all aspects of operations in the U.S. Senate and a career that spans military intelligence to cyber operations, Gibson’s address highlights a fundamental challenge for cybersecurity leaders: protecting what cannot always be seen or controlled. From legacy systems and outdated technology to HR practices and dependencies on third-party providers, she examines how hidden vulnerabilities accumulate—and what leaders can do to better understand risks, strengthen resilience, and protect the mission.
The Program: From Shadow IT to Quantum Computing to Artificial Intelligence
This year’s IT Security Conference is themed «Shadow IT.» When employees—whether out of genuine interest or a desire to get their work done despite restrictive guidelines—turn to IT solutions that aren’t officially approved or managed, this can certainly be productive. At the same time, however, shadow IT poses significant risks to security and compliance. This year’s program also features other current topics, such as artificial intelligence and quantum computing.
The following speakers will present their insights and latest research findings at Swiss Cyber Storm 2026: Stéphane Adamiste has been analyzing Switzerland’s e-voting system for years and will present his key findings as well as an assessment of the system’s security. Mazin Ahmed of Fullhunt.io has investigated the attack surface throughout Switzerland specifically for the conference and discovered a large number of shadow IT systems in the process. Marco Brenner works at IBM on quantum computers—a topic that is no longer far in the future but is often approached incorrectly. Nadim Kobeissi will introduce his software «Verifpal» and demonstrate how it can be used to analyze complex protocols even without in-depth knowledge of cryptography. Felix Linker is working on the Red Cross’s digital emblem, which aims to make the organization’s online infrastructure visible and identifiable to attackers.
Hannes Lubich classifies various forms of shadow IT into a taxonomy and explains how companies should deal with them. Loïc Maréchal has examined the cyber research landscape in Swiss industry, presents his gap analysis, and provides access to his data. Andreas Maurer focuses on digital fraud—a topic that is currently also of concern to FINMA—and introduces his «Trident Resilience Framework.» Michael Morgenstern has new data on «shadow AI» in companies and presents ideas on how to tackle the problem. Benjamin Rothenberger explains how the post-quantum problem will fundamentally change the way browsers use encryption—a change that must go beyond simply replacing a few algorithms.
Sébastien Schnyder observes criminals at work using Google AI, illustrates their methods with concrete examples, and explains what lessons can be learned from them. Ivano Somaini is a pioneer in the use of technology in the field of OSINT and shows what new avenues artificial intelligence is opening up. Jeroen van der Ham-de Vos has extensive experience in vulnerability management—a field that has come under new pressure due to AI—and explains what needs to be done now. Tin Zaw takes a close look at HTTP traffic, identifies bot traffic as «shadow traffic,» and highlights what can be done about it today.
Dutch behavioral analyst An Gaiser will conclude the event and discuss various aspects of deepfakes in her keynote address. In doing so, she challenges one of the most persistent notions in cybersecurity: that humans are the weakest link in the chain. She has some provocative theories to share on this topic.
About Swiss Cyber Storm
Over the many years of its existence, Swiss Cyber Storm has established itself as Switzerland’s leading IT security conference and today sets the agenda for the Swiss security industry. At the event, international experts present the latest insights to a diverse national audience consisting of students, tech enthusiasts, and IT security leaders. While other conferences often focus on vulnerabilities, Swiss Cyber Storm provides the broader context and presents practical, proven solutions to structural security problems.